Expert Interview: Why Information Security Governance Has Become a Business Imperative
Organizations managing sensitive information face growing expectations from customers, regulators, and business partners to demonstrate that their security and privacy controls are governed and operating effectively. As organizations rely more heavily on data and emerging technologies to support business decisions, independent assurance has become an important way to provide objective validation that security and privacy controls are designed appropriately and operating effectively.
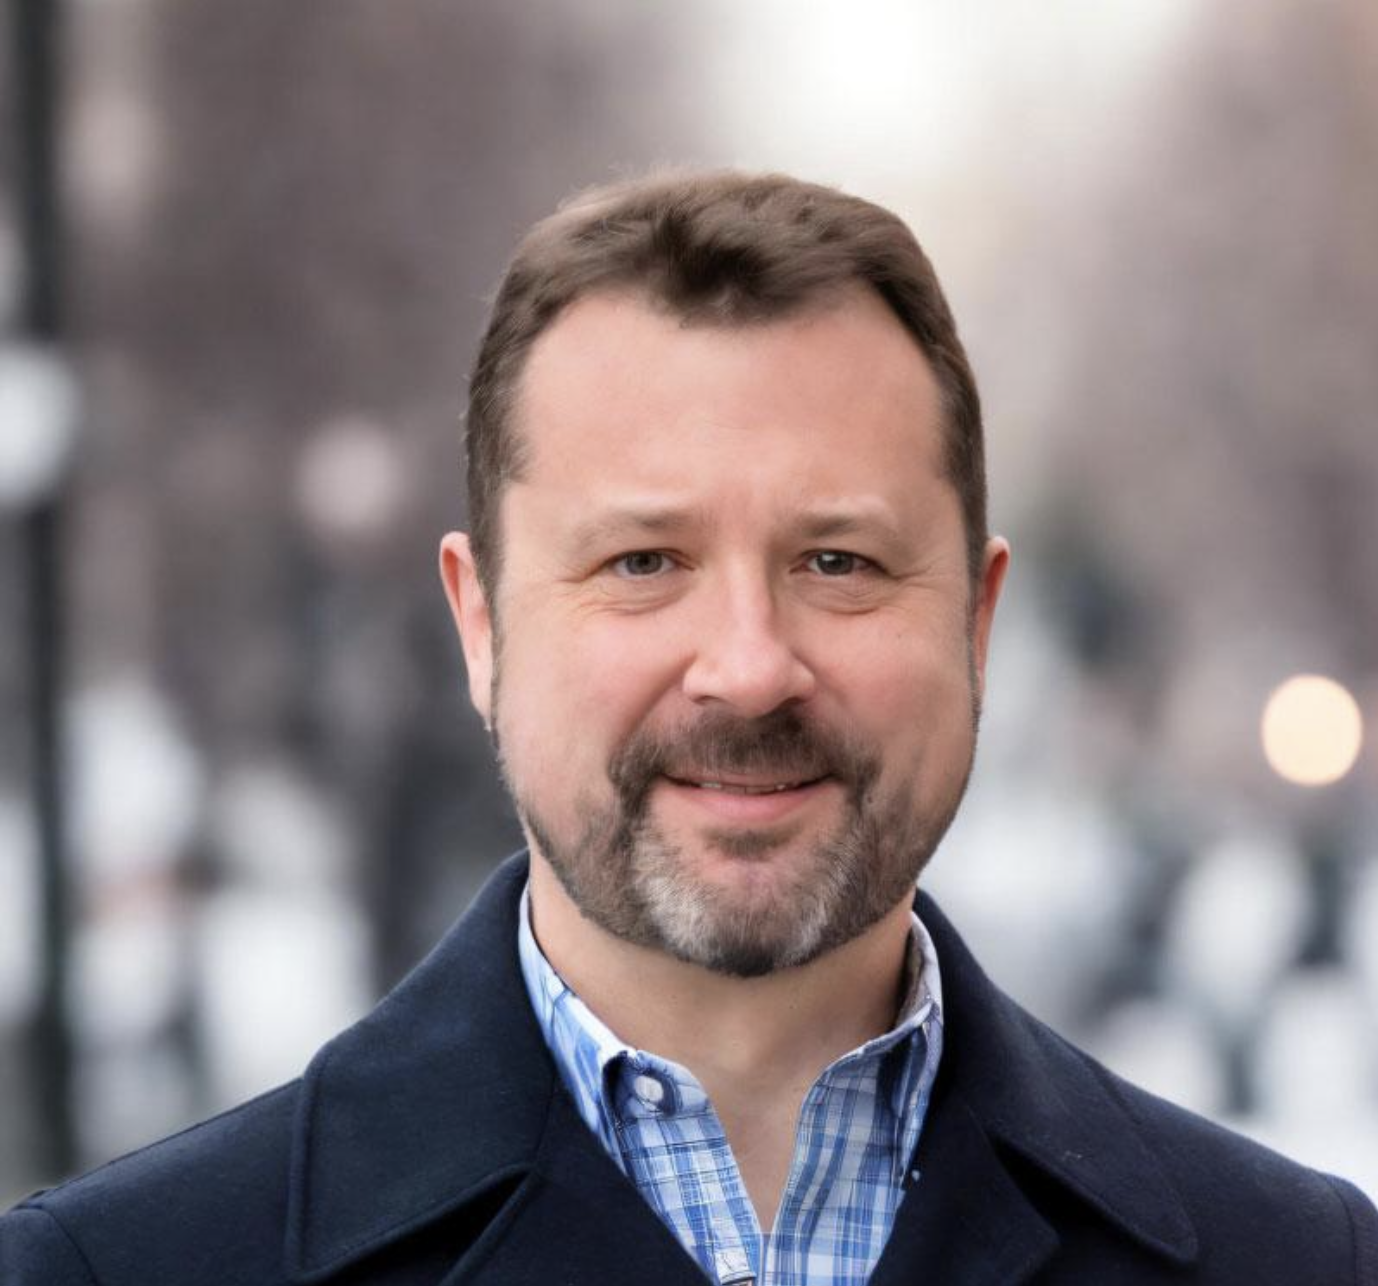
We recently sat down with Josh Daymont, CEO of Securisea. Securisea was the first organization to achieve FedRAMP 3PAO accreditation under A2LA’s revised two-step process and is one of only 50 organizations nationwide currently holding that accreditation. We spoke with Josh about how these expectations are changing, why independent assurance has become increasingly important, and what organizations should consider as they prepare for future assurance engagements.
Q: Enterprise customers are asking more questions about information security governance before they sign contracts. What has changed?
Josh: Organizations are being evaluated differently than they were several years ago. Customers want confidence that security and privacy controls are designed appropriately, operating effectively, and subject to real oversight. Those expectations often extend beyond regulatory requirements and become part of procurement, vendor risk management, and executive decision-making.
As a result, information security governance is becoming a core business consideration rather than something organizations address only when a specific requirement arises.
Q: How has that changed the role independent assurance plays?
Josh: Independent assurance gives organizations an objective evaluation of their control environment. Whether the engagement is a SOC examination, a FedRAMP security assessment, or a HITRUST validated assessment, stakeholders rely on the results because the work is performed independently and follows an established methodology.
As these expectations continue to grow, organizations increasingly view independent assurance as part of demonstrating credibility with customers, business partners, and regulators.
Q: Where do organizations most often misunderstand assurance expectations?
Josh: One common misconception is assuming that different assurance frameworks are interchangeable or that they all evaluate organizations in the same way. Each framework has a specific purpose, its own methodology, and distinct reporting objectives.
Organizations are generally better prepared when they understand what an engagement is intended to evaluate, how evidence will be assessed, and what stakeholders expect from the resulting report or certification.
Q: You’ve worked with organizations operating under some of the most demanding assurance requirements. What lessons from those environments apply more broadly?
Josh: Highly regulated assessment programs place significant emphasis on consistency, documented methodologies, and objective evaluation. While every framework has different requirements, those principles apply across many types of assurance engagements.
Organizations are better positioned when they understand not only the requirements themselves, but how those requirements are evaluated during an independent assessment, including what evidence an assessor will request and how sampling and testing decisions get made.
Q: How do you see AI governance expectations developing over the next several Years?
Josh: Organizations are moving quickly to adopt AI, but AI governance expectations are evolving just as quickly. Leadership teams are thinking more about accountability, oversight, risk management, and how AI fits within existing information security governance structures.
Independent assurance will continue to play an important role because organizations need objective evaluations of the controls and oversight processes supporting those technologies, just as they do for other business-critical systems.
Q: What should executive teams be thinking about today that they may not have been thinking about five years ago?
Josh: Information security governance has become an ongoing business capability rather than a periodic exercise. Customers, regulators, and business partners increasingly expect organizations to demonstrate that oversight processes are established, consistently applied, and supported by independent evaluation where appropriate.
Organizations that approach governance proactively are generally in a stronger position to respond to changing requirements, support business growth, and build long-term trust with stakeholders.
Learn more about the independent assurance engagements Securisea performs at www.securisea.com.